
Test Auth Flows
This section guides you through verifying your auth endpoints.
Tests not working?If you need assistance, contact us and our team will work with you to find a solution.
With your authentication endpoints implemented, we will now test basic authentication flows to verify the configuration.
Test 1: Verify Signup Flow
Follow these steps to test the Application-Level Signup flow:
- Select your application from the Dashboard Home Page.
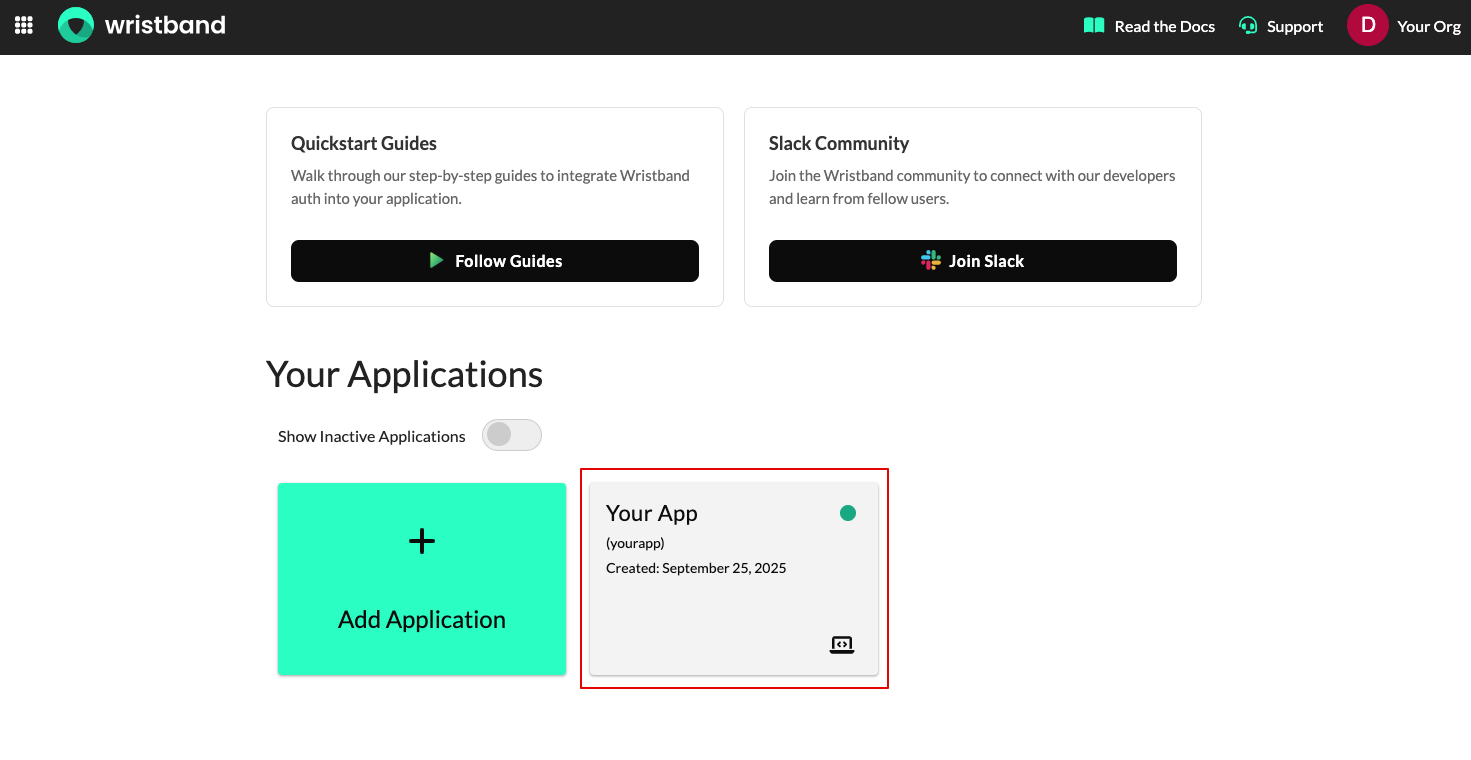
Figure 1: Select your Wristband application.
- On the Application Settings page, expand the Application URLs accordion and click the external link icon next to the Application-level Signup URL field.
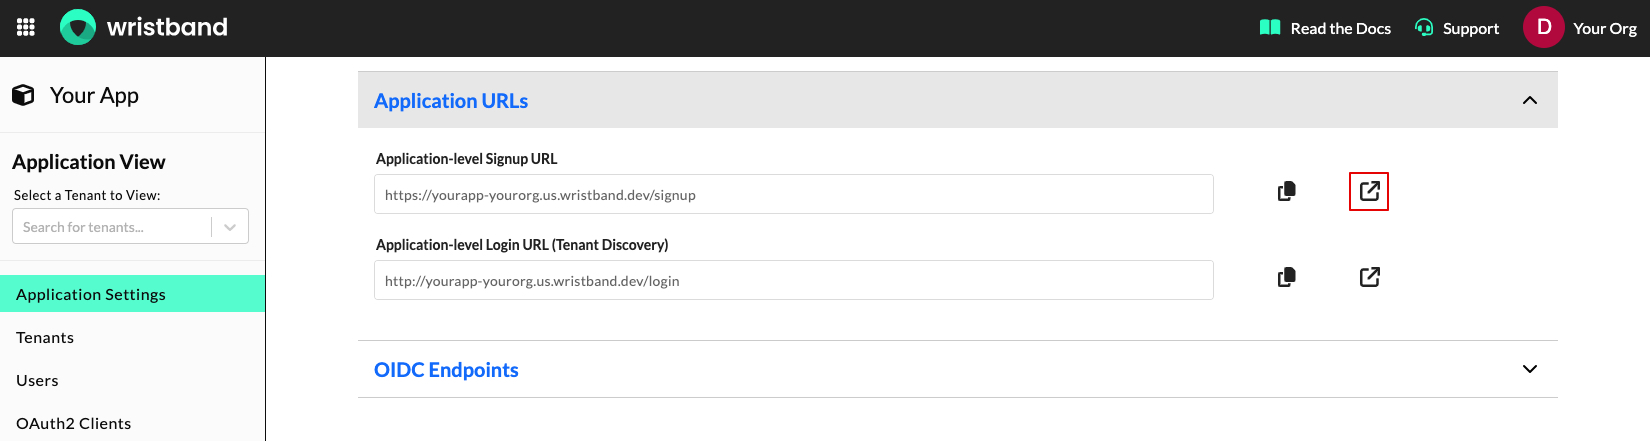
Figure 2: Open the Application-level Signup URL.
-
The Application-Level Signup page will open in a new browser tab. Fill out the following fields on that page:
- Tenant Name - Application-level signup creates a new tenant under your application. This will be the name of the tenant that is created.
- Email - A valid email address under your possession. To complete the signup process, you'll need to view an activation email sent to this address.
- Password - The password that you will use to log in.
- When finished, click the Sign Up button.
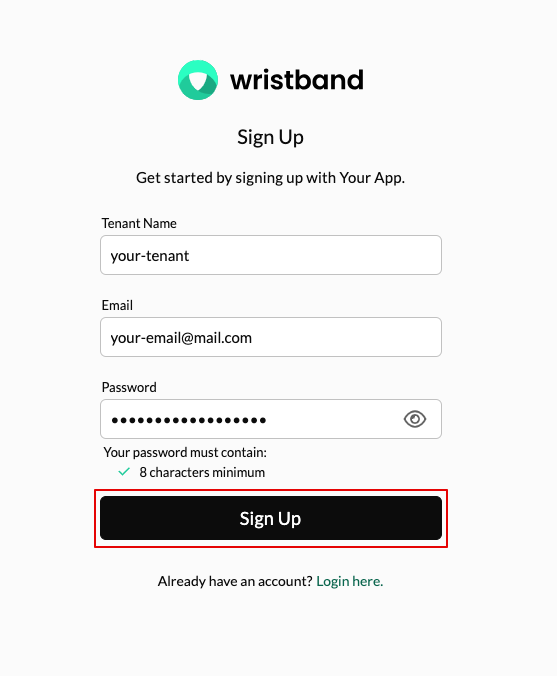
Figure 3: Complete the signup form.
- You will receive an email containing a one-time code. Enter this code into the Verification Code field and click Verify.
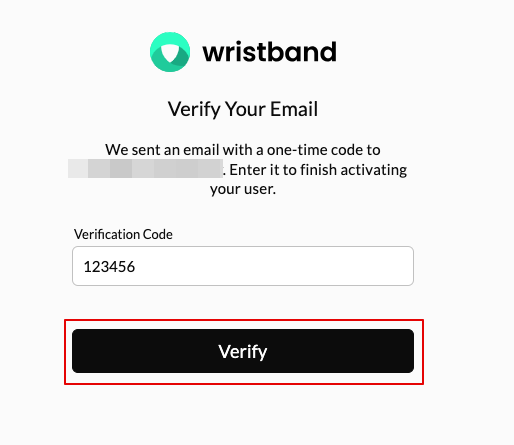
Figure 4: Verify the signup email address.
- A successful signup redirects you to your application's home page (or the default return URL configured in your Callback Endpoint).
Congratulations—you have successfully completed the Application-Level Signup flow! Here is a look at what just happened behind the scenes:
- A new tenant was created under your application with the "Tenant Name" that you provided.
- A new user was created under the tenant with the email and password that you specified.
- The user was activated using an email containing a verification code.
- A Wristband auth session was created for the user.
Test 2: Verify Login Flow
Before testing the user login flow, ensure no active Wristband auth sessions exist for your newly created user. An active session will trigger automatic authentication upon hitting the tenant login page, bypassing the login screen.
Clearing the User's Active Auth Sessions
Complete the following steps to clear the active auth sessions:
- Select your application from the Dashboard Home Page.
Figure 5: Select your Wristband application.
- Next, select Users from the navigation bar and then select the user that was created through the signup process from the Users table.
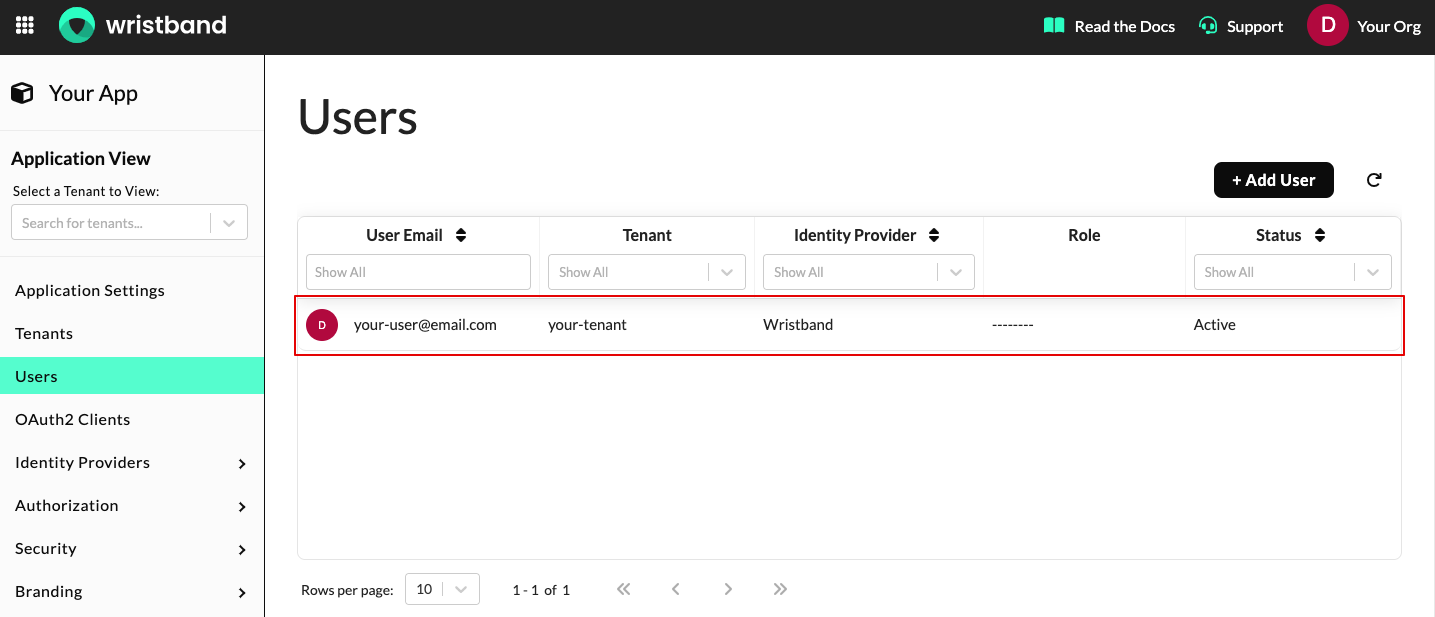
Figure 6: Select the new user.
- On the Edit User screen, scroll down to the Active Auth Sessions section and click the Delete Sessions button.
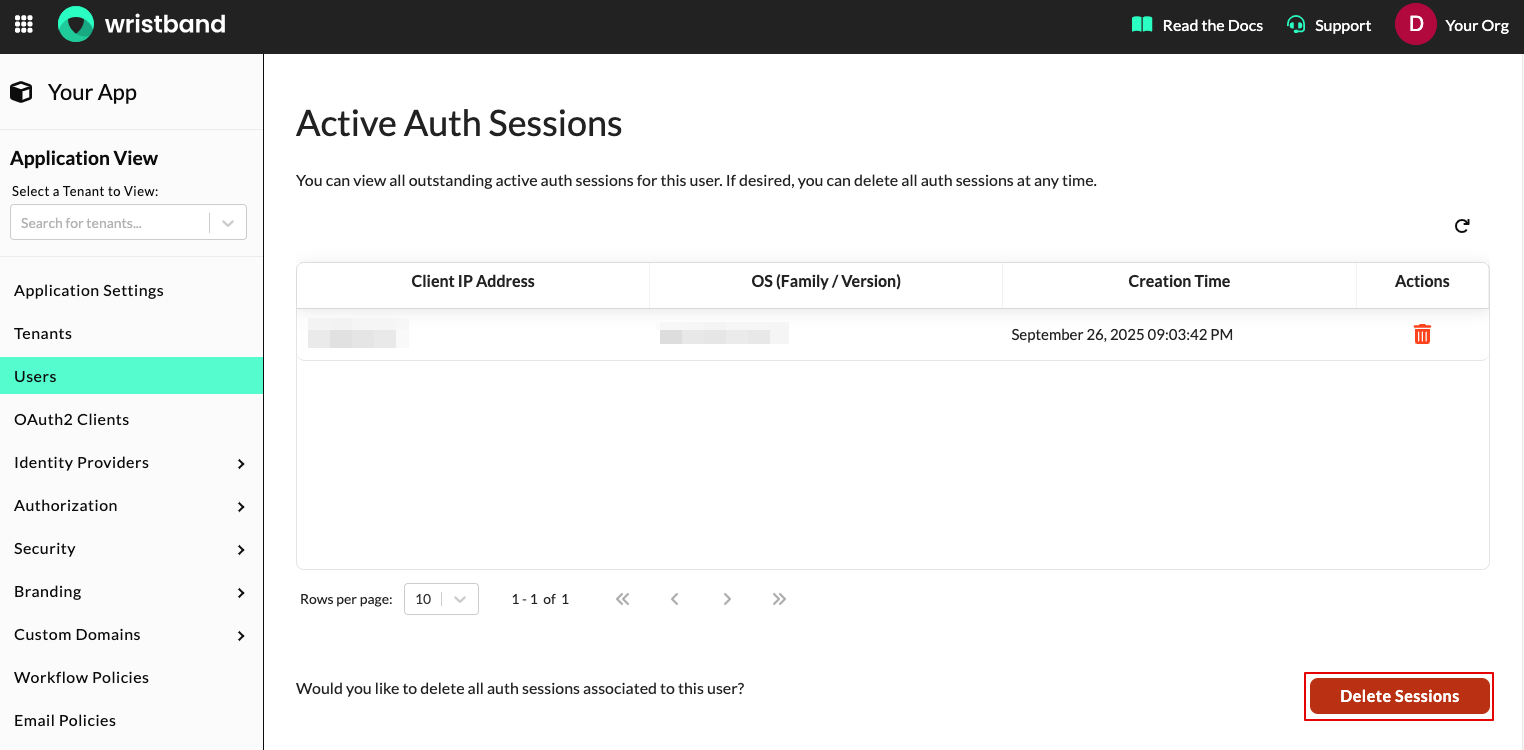
Figure 7: Clear the user's active auth sessions.
Perform User Login
With the active auth sessions cleared, you can now test the login flow by following these steps:
- Select your application from the Dashboard Home Page.
Figure 8: Select your Wristband application.
- On the Application Settings page:
- Expand the Application URLs section.
- Click the external link icon next to the Application-level Login URL.
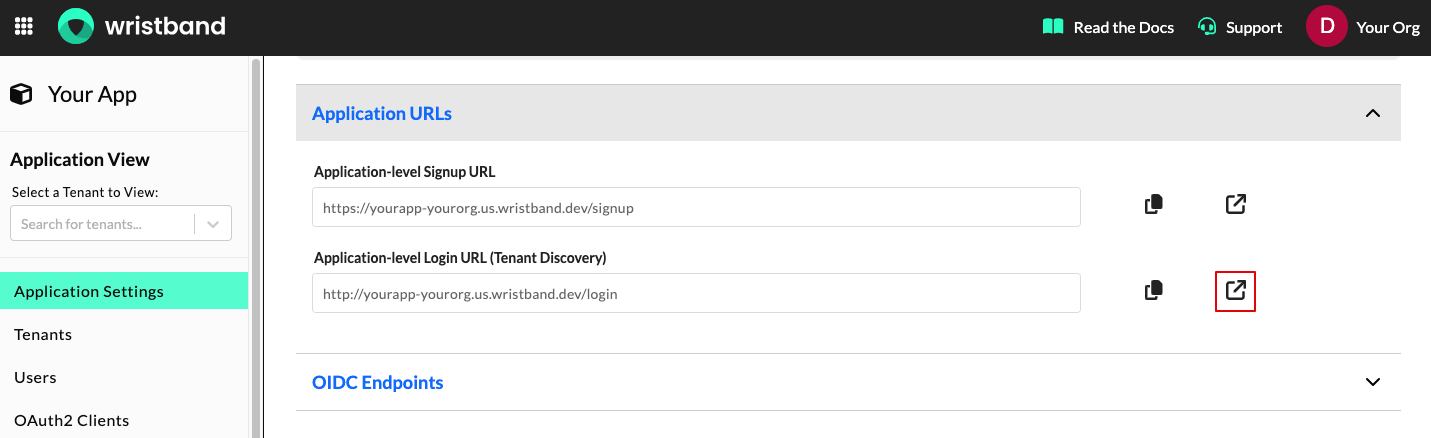
Figure 9: Open the Application-level Login URL.
- In the new browser tab that opens:
- View the Application-Level Login page.
- Locate the tenant you created during the signup flow and click Select.
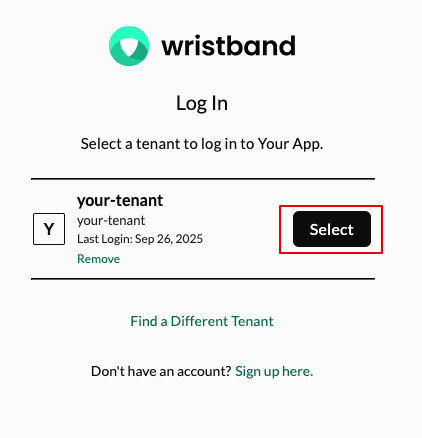
Figure 10: Select your tenant.
- On the tenant login page:
- Enter the email and password for your newly created user.
- Click the Log In button.
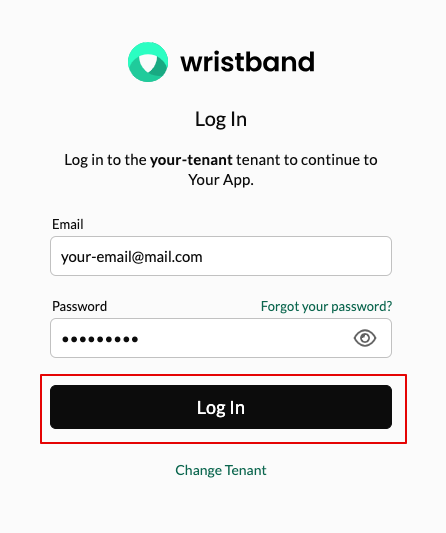
Figure 11: Log in as the new user.
- If the login succeeds, you'll be redirected to your application's default home page. This matches the final redirect URL you established during the Add Auth Endpoints step.
Test 3: Verify Auth Session
The active session is now established. When hitting the tenant login page again, Wristband's session detection will bypass the login prompt. Complete these steps to observe the automated flow:
• Retrieve your Application-level Login URL from the Application URLs section on the Application Settings page.
• Enter this URL into your browser to load the login page.
Figure 12: Open the application-level login URL.
- On the Application-Level Login page:
- Locate the tenant you previously logged in to.
- Click the Select button next to it to be redirected to that tenant's login page.
Figure 13: Select the tenant you created during signup.
- Because an active auth session is already established for this tenant, you will bypass the credential prompt and be automatically redirected to your application's home page (or the return URL specified in your Callback Endpoint).
Test 4: Verify Logout
Now, let's run the logout flow to terminate the user's active auth session. Follow these steps to log out:
- In your browser's address bar, enter the URL of your Logout Endpoint (e.g.,
http://localhost:3001/auth/logout) and press Enter to navigate to it. This will cause the logic within your Logout Endpoint to execute. - At the end of the logout flow, you should be redirected to your tenant's login page.
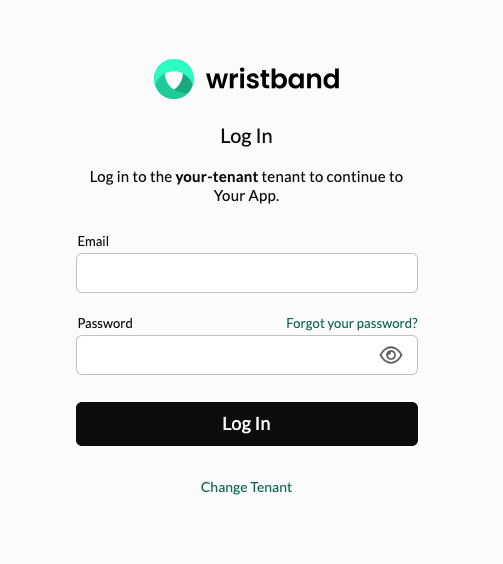
Figure 14: After logout, Wristband prompts the user to sign in again.
- Seeing the tenant login page prompt for your credentials confirms that the user's auth session has been terminated and the logout flow executed successfully.
Congratulations! Reaching this point means your auth endpoints are working correctly.
Test 1: Verify Signup Flow
First, we'll test the Application-Level Signup flow. To do so, please perform the following steps:
- Select your application from the Dashboard Home Page.
- On the Application Settings page, scroll down to the Application URLs section and click the header to expand the accordion menu. Within the Application URLs section, click the external link icon next to the Application-level Signup URL field.
-
After clicking the external link icon, a new browser tab will open showing the Application-Level Signup page. Fill out the following fields on that page:
- Tenant Name - Application-level signup creates a new tenant under your application. This will be the name of the tenant that is created.
- Email - A valid email address under your possession. To complete the signup process, you'll need to view an activation email sent to this address.
- Password - The password that you will use to log in.
When finished, click the "Sign Up" button.
- Next, you should get an email containing a one-time code. Enter the code into the Verification Code form field and then click the "Verify" button.
- If the signup process succeeds, you'll be redirected to the URL you specified as the final redirect in your Callback Endpoint (set up in the Add Auth Endpoints step). This is typically your application's home page.
Congratulations, you just completed the Application-Level Signup flow! Behind the scenes, the following operations were performed.
- A new tenant was created under your application with the "Tenant Name" that you provided.
- A new user was created under the tenant with the email and password that you specified.
- The user was activated using an email containing a verification code.
- A Wristband auth session was created for the user.
Test 2: Verify Login Flow
Next, let's test the user login flow. Before doing so, ensure the user you just created doesn't have any active Wristband auth sessions (they likely do if you have just completed the signup flow). If an active session exists, the user will be automatically authenticated when navigating to their tenant login page, bypassing the login screen (which we don't want for this test).
Clearing the User's Active Auth Sessions
To clear the user's active auth sessions, perform the following steps:
- Select your application from the Dashboard Home Page.
- Next, select "Users" from the navigation bar and then select the user that was created through the signup process from the Users table.
- On the Edit User screen, scroll down to the Active Auth Sessions section and click the "Delete Sessions" button.
Perform User Login
Now that we've cleared the user's active auth sessions, we can test the login flow. To do so, please perform the following steps:
- Select your application from the Dashboard Home Page.
- On the Application Settings page, scroll down to the Application URLs section and click the header to expand the accordion menu. Within the Application URLs section, click the external link icon next to the Application-level Login URL field.
- After clicking the external link icon, a new browser tab will open to the Application-Level Login page. This page lists the tenants you've previously authenticated with. Click the "Select" button next to the tenant you created during the signup flow.
- You should now see the login page for the selected tenant. Enter your email and password for the user you created during the signup flow, then click the "Log In" button.
- If the login process succeeds, you'll be redirected to the URL you specified as the final redirect in your Callback Endpoint (set up in the Add Auth Endpoints step). This is typically your application's home page.
Test 3: Verify Auth Session
After successfully logging in, your user should now have an active Wristband auth session. If you revisit the tenant login page, Wristband will detect your user's active session and skip the login screen that prompts for credentials. To test this behavior, please perform the following steps:
- Enter your application-level login URL into your browser to navigate to the Application-Level Login page. If you don't have your application-level login URL on hand, you can find it on the Application Settings page, under the Application URLs section.
- On the Application-Level Login page, you'll see a list of tenants you've previously authenticated with. Click the "Select" button next to the tenant you previously logged in to. This will redirect you to that tenant's login page.
- Since your user already has an active auth session for this tenant, you should not be prompted for credentials. Instead, you'll automatically be logged in and redirected to the URL specified at the end of your Callback Endpoint, which is typically your application's home page.
Test 4: Verify Logout
Now, let's run the logout flow to terminate your user's Wristband auth session. To execute the logout flow, perform the following steps:
- In your browser's address bar, enter the URL of your Logout Endpoint (e.g.,
http://localhost:3001/auth/logout) and press Enter to navigate to it. This will cause the logic within your Logout Endpoint to execute. - At the end of the logout flow, you should be redirected to your tenant's login page.
- The fact that the tenant login page is now prompting for your credentials indicates that your user's auth session has been terminated and that the logout flow executed successfully.
If you've reached this point, congratulations! Your auth endpoints are working correctly. 🎉
Looking good. You're starting off just fine.
Updated 14 days ago
What’s Next
Now that you've verified your auth flows are working, let’s secure your frontend routes and components so only authenticated users can access them.