
Identity Providers
Identity providers (IdPs) are services that verify user identities and manage their login credentials.
Identity providers (IdPs) authenticate users and manage their digital identities. To allow users to log in to your application, you must configure at least one IdP. While Wristband is enabled as your default identity provider, you can connect external IdPs to let users authenticate using their existing credentials.
The following sections detail the different types of identity providers supported by Wristband.
Wristband Identity Provider
Wristband acts as your default IdP and is automatically enabled when you create a new application. You can configure the built-in Wristband IdP to support various combinations of login identifiers and authentication factors:
Supported Login Identifier Permutations
- Email Only: Users authenticate by providing their email address as their primary login identifier.
- Email or Username: Users can identify themselves by entering either their email address or their unique username.
Supported Login Factor Permutations
- Password: Users are required to log in with a password, which you can configure by following the steps in the Passwords documentation.
- Magic Link: Users authenticate by entering their email address to receive a one-time login link via email, which you can configure using the Magic Links documentation.
- Password or Magic Link: Users have the flexibility to log in using either their password or a passwordless magic link.
Multi-Factor Authentication (MFA)
Configure multi-factor authentication for the Wristband IdP globally or per-tenant using MFA policies. Application-level policies apply to all users across the app, while tenant-level overrides isolate settings to a specific tenant.
MFA policies allow you to control the following configurations:
-
MFA Enrollment Requirements: When MFA enrollment is mandatory, users must set up their second factor before they can complete authentication. The following workflows automatically prompt unenrolled users to register:
- User invite
- Password reset (if immediate login is enabled)
- Login
- Signup
-
Enabled MFA Factors: MFA policies allows you to select which multi-factor authentication methods are active. Wristband currently supports the following options:
- TOTP: Users must provide a Time-based One-Time Password (TOTP) from an authenticator app like Google Authenticator or Authy. This factor is currently required whenever MFA is enabled.
- Recovery Code: Upon completing enrollment, users receive a backup code to access their account if they lose access to their primary authentication device.
-
Issuer: Customize the issuer name displayed in authenticator apps during TOTP enrollment. Leave this field blank to default to your application's display name.
For complete setup steps and policy options, see the Multi-Factor Authentication (MFA) documentation.
NoteMFA policies only apply to users authenticating directly through Wristband, not those using an external identity provider (IdP). If you require multi-factor authentication for external IdP users, you must configure and enforce those MFA requirements directly within that external provider's settings.
External Identity Providers
Wristband supports integrations with external Identity Providers (IdPs), allowing users to log in using an existing account. These external IdPs are grouped into two categories:
- Social Identity Providers
- Enterprise Identity Providers
The sections below outline the specific identity providers supported within each category.
Social Identity Providers
Social identity providers allow users to authenticate using personal accounts managed by popular cloud services. This login method is ideal for consumer-facing apps or product-led growth (PLG) B2B platforms where individuals self-onboard.
Wristband supports the following social identity providers:
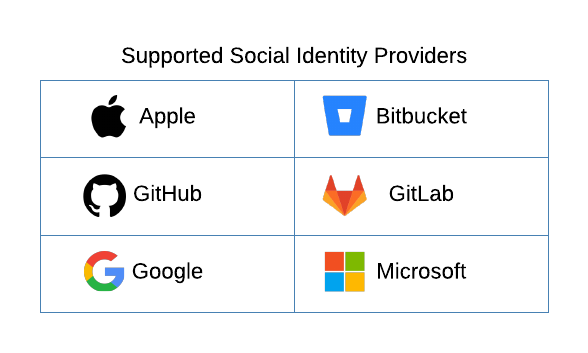
Figure 1: Social identity providers supported by Wristband.
For detailed configuration steps, please see the Configuring Social Identity Providers documentation.
Enterprise Identity Providers
Enterprise identity providers allow users to authenticate using credentials managed by an external organization, typically their employer. These integrations enable Single Sign-On (SSO) so employees can securely access your application using their existing workplace credentials.
Enterprise IdPs are typically integrated using either the SAML 2.0 or OIDC protocol. The table below lists the enterprise IdPs supported by Wristband along with their compatible protocols:
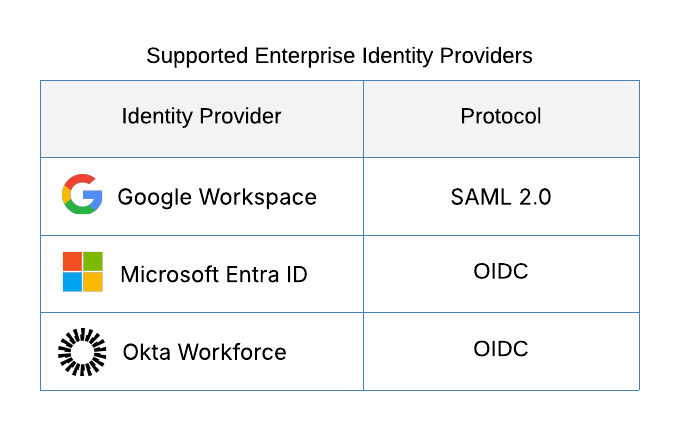
Figure 2: Enterprise identity providers supported by Wristband and their compatible SAML 2.0 or OIDC protocols.
For detailed setup steps, please see the Configuring Enterprise Identity Providers documentation.
Custom Identity Providers
If an organization uses an identity provider that Wristband does not support out of the box, you can still integrate it by configuring a custom identity provider. Wristband currently supports custom integrations using the following protocols:
- SAML 2.0
Note:Enterprise identity providers must be configured at the tenant level to tie them to a specific external organization. The only exception is Global Tenants, which cannot use enterprise IdPs because they are designed for users who are not associated with any organization.
Tenant-Level Overrides
You can override identity providers at the tenant level, allowing different tenants to have different identity providers enabled.
To configure a tenant-level override, switch from Application View to Tenant View by selecting a tenant from the dropdown in the side navigation menu. From there, navigate to Identity Providers and turn on the tenant override toggle.
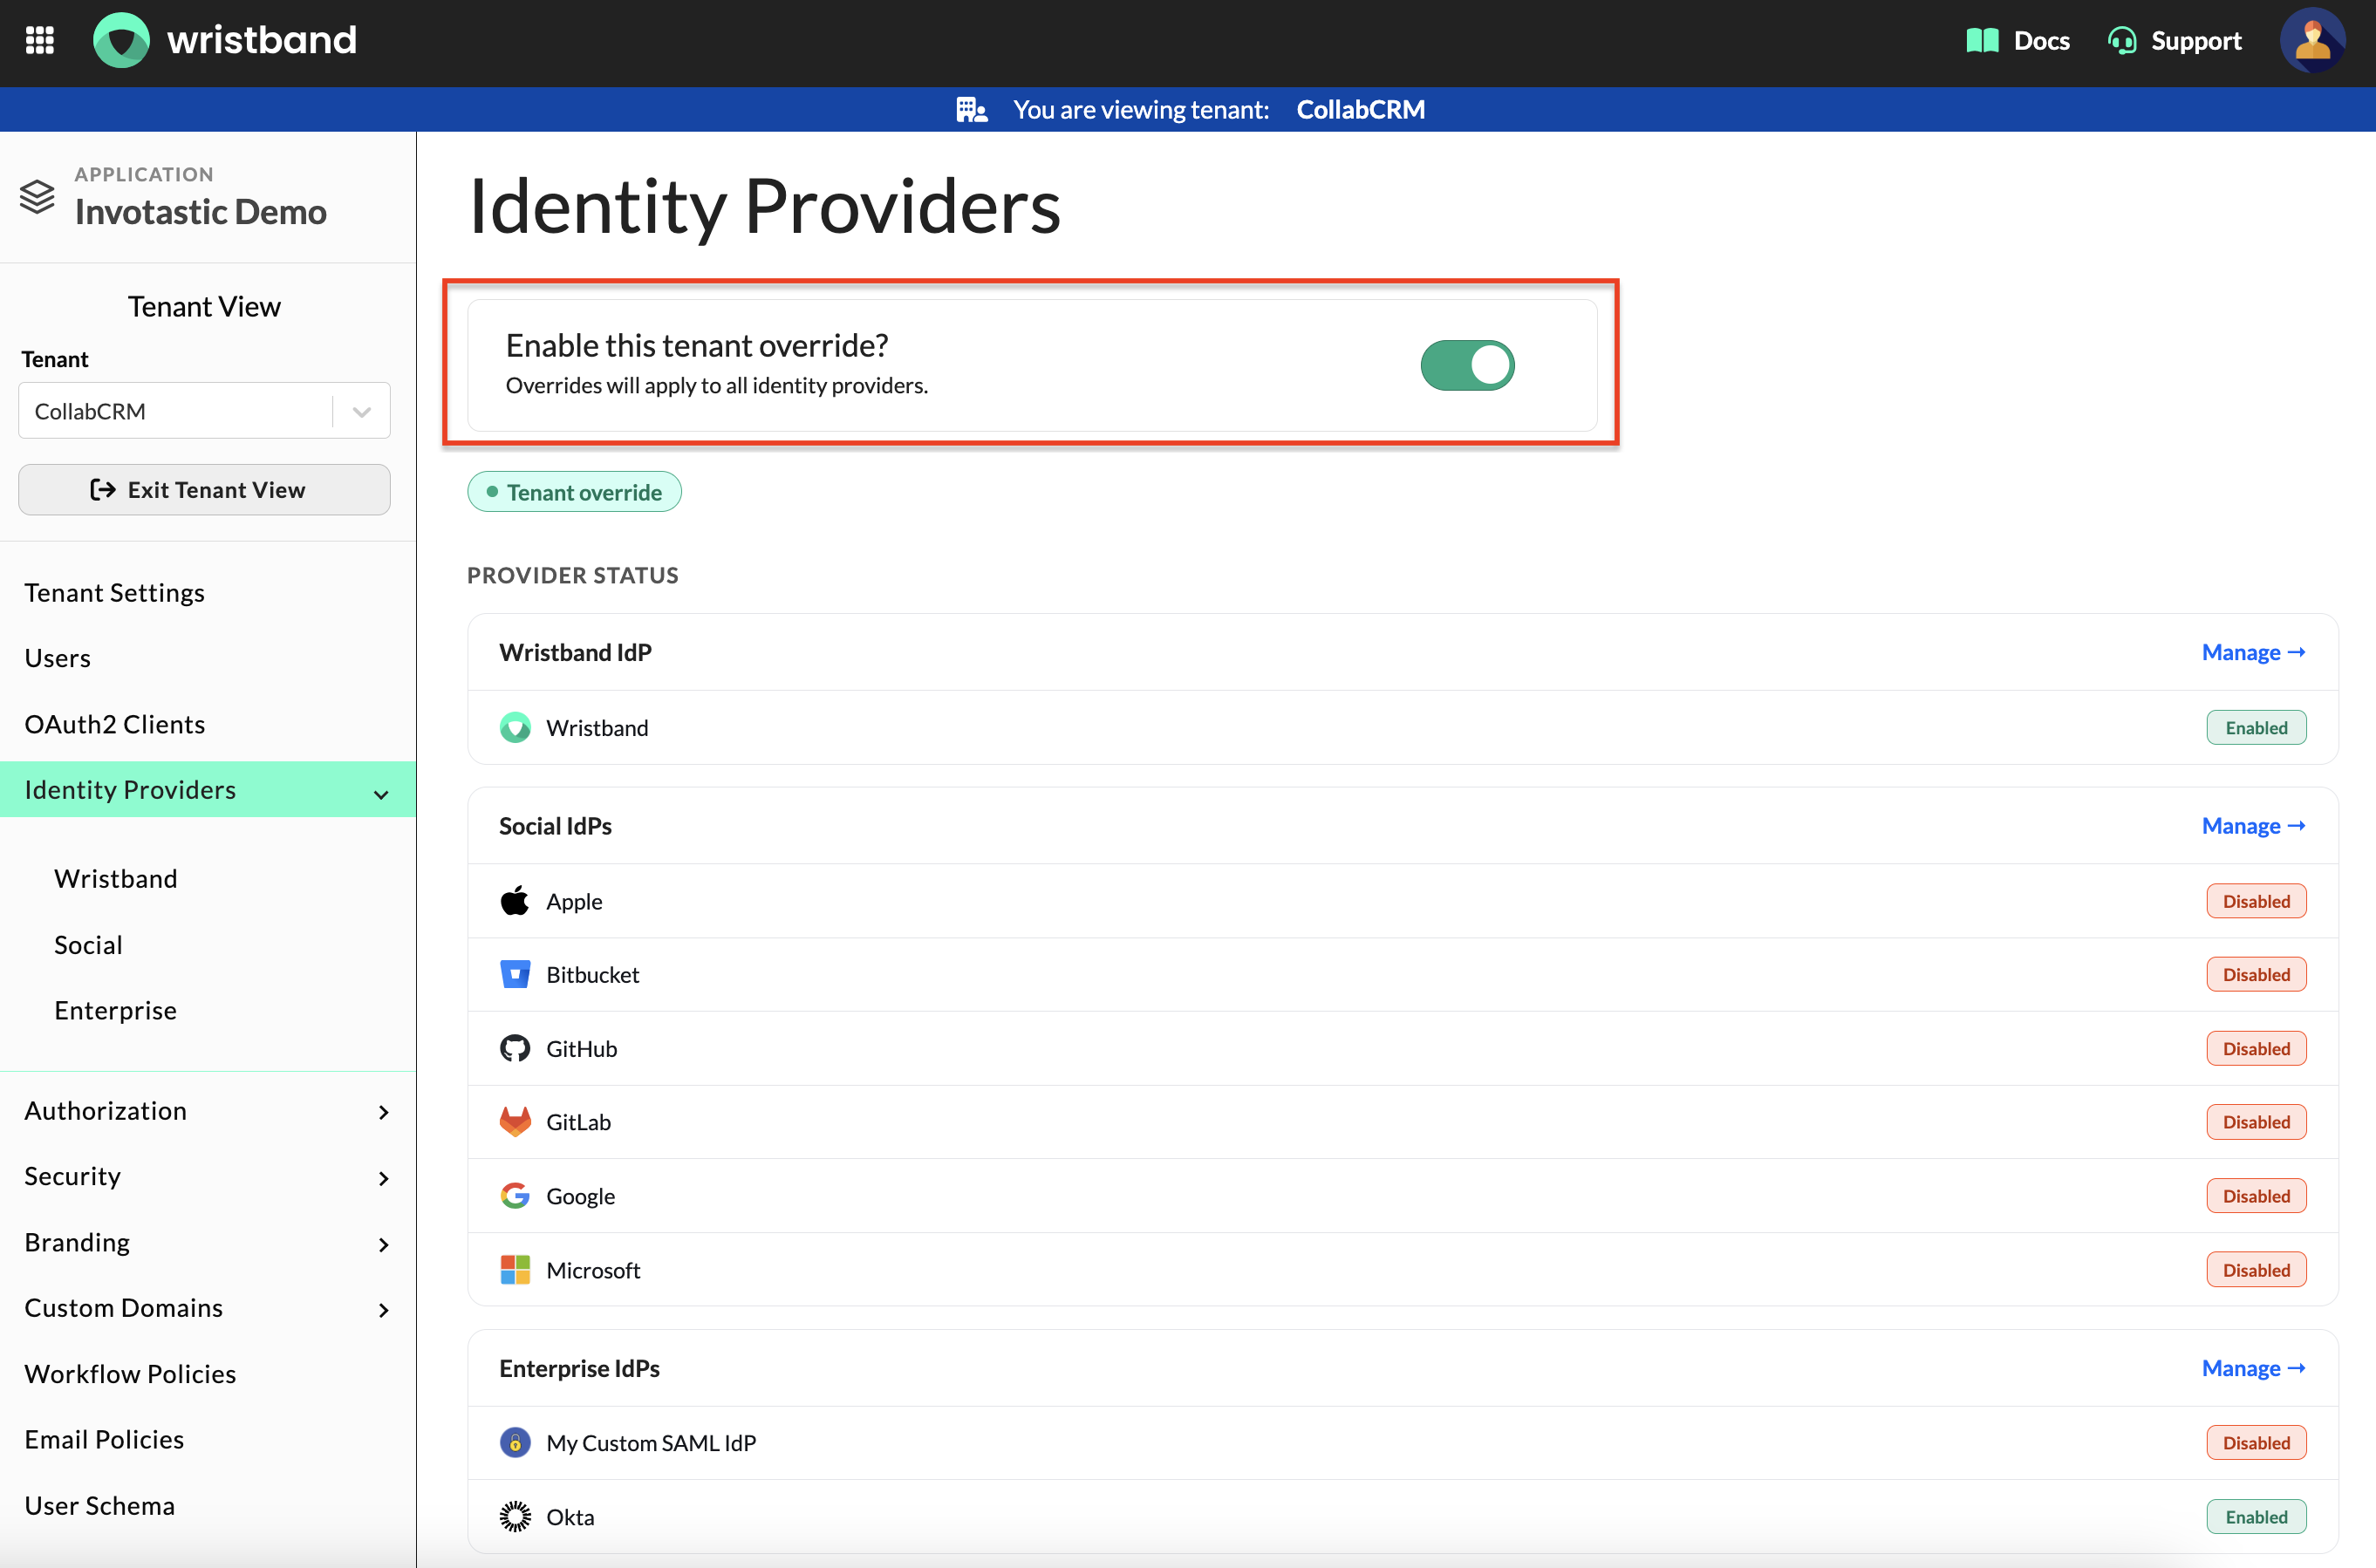
Figure 3: Enable the tenant-level identity provider override to use a tenant-specific IdP configuration.
Updated 9 days ago